Free Lesson
MCP Security Horror Stories: AI Agents vs. Your Product
60 min
Nov 13, 2026 12:30 PM
By continuing, you agree to Maven's Terms and Privacy Policy.
What you'll learn
How to spot the risks an MCP server adds to your product
Learn the main risks: tools that reach too much data, tools that delete it, weak auth, and fake MCP servers.
How to recognize prompt injection and malicious MCP servers
See how each documented attack worked, what it taught us, and how to avoid making the same mistake.
How to limit what agents can do through your MCP server
Choose which tools stay read-only, which need a person to approve, and what data each user's agent can reach.
How to use the OWASP MCP Top 10 before you ship
Learn what each of the ten risks means for your product and leave with a checklist you can share with your team.
What's solved in MCP security and what still isn't
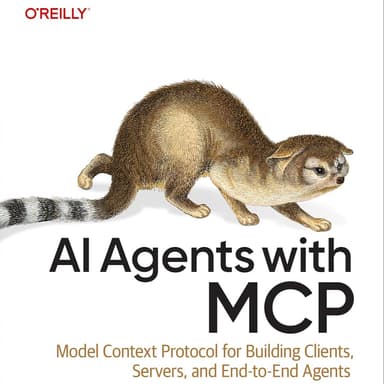
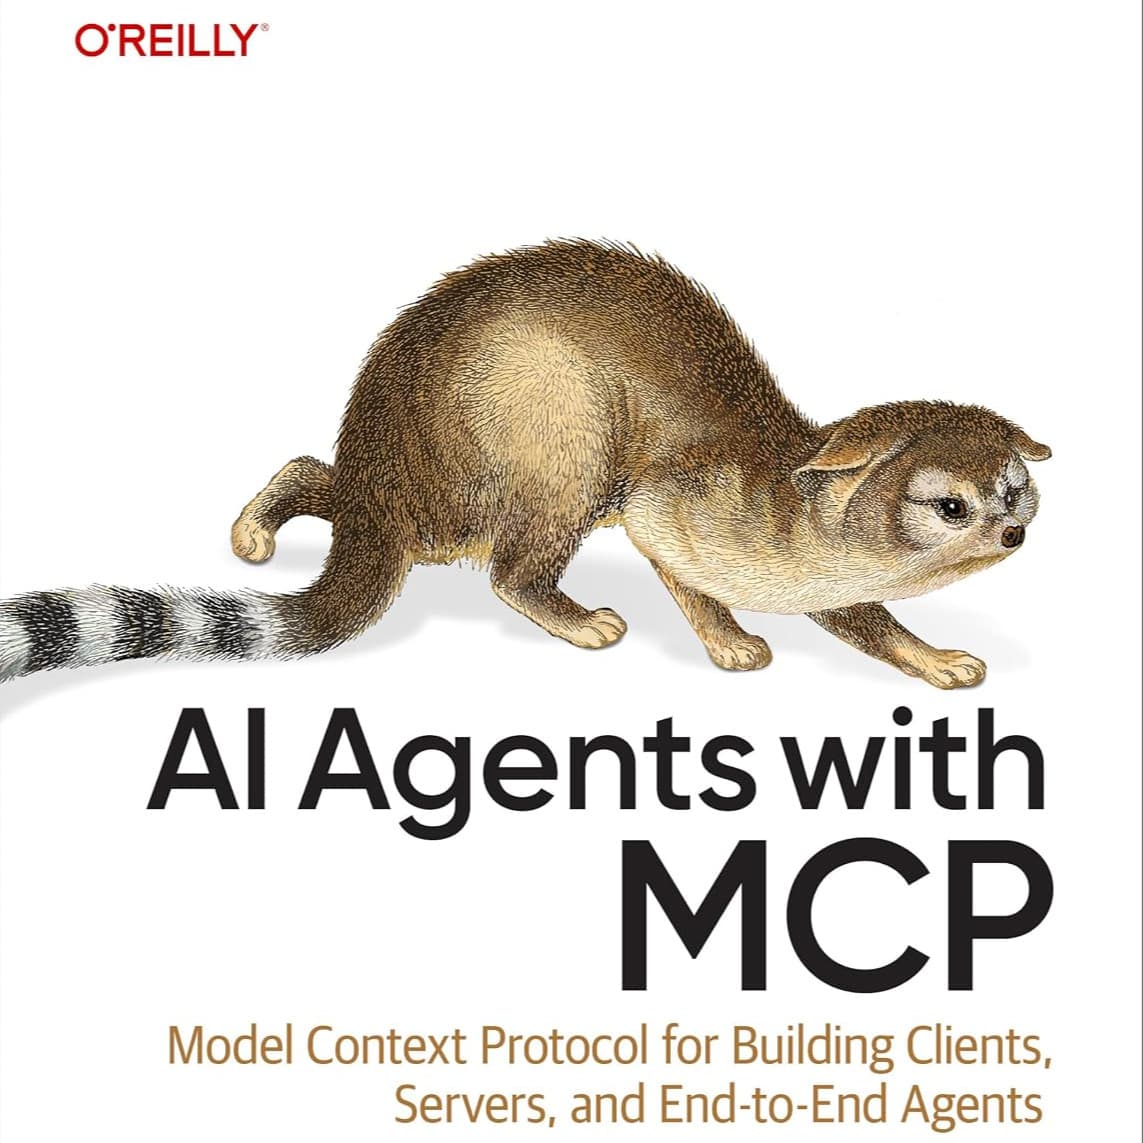
Get Kyle's read, as author of O'Reilly's AI Agents with MCP, on what the latest spec fixes and where to learn more.
Why this topic matters
Your MCP server hands AI agents your customers' data and the power to act on it. A tool scoped too broadly leaks that data, a vague one deletes it, weak auth lets the wrong people in, and a look-alike server steals it. On Friday the 13th, Kyle Stratis, author of O'Reilly's AI Agents with MCP, joins Emmanuel to walk through the MCP horror stories so far and how to avoid each one. You'll leave with a checklist to run on Monday.